ZUBIQO.
AI & MLCryptoFinanceBig TechAI Models
CybersecurityGamingEVs & Clean EnergyRoboticsAerospaceBiotech & Health
Enterprise
ZUBIQO.

High-magnitude intelligence briefs for the tech and finance sectors. Zero fluff. Maximum signal.

[email protected]
X (Twitter)ThreadsTelegramBlueskyMastodon

Sections

  • AI & ML
  • Crypto
  • Finance
  • Big Tech
  • Cybersecurity
  • Gaming
  • EVs & Clean Energy
  • Robotics
  • Aerospace
  • Biotech & Health

Publication

  • About Us
  • Editorial Ethics
  • Partner With Us
  • Contact Us

Tools

  • AI Models Pricing

Legal

  • Privacy Policy
  • Terms of Service
  • Fair Use & DMCA

Disclaimer:Zubiqo Intelligence operates as a technology-enabled news and research publication under human editorial oversight. The news briefs, market analysis, "Magnitude Scores", and "Community Sentiment" metrics provided on this platform are strictly for informational and educational purposes only. They do not constitute financial, legal, investment, or trading advice. Cryptocurrencies and financial markets are highly volatile; always conduct your own research and consult with a licensed professional before making any investment decisions. By using this site, you agree to our Terms of Service.

© 2026 Zubiqo Intelligence. All rights reserved.

CybersecurityMAG 6Bearish
•
2026-09-18•1 min read

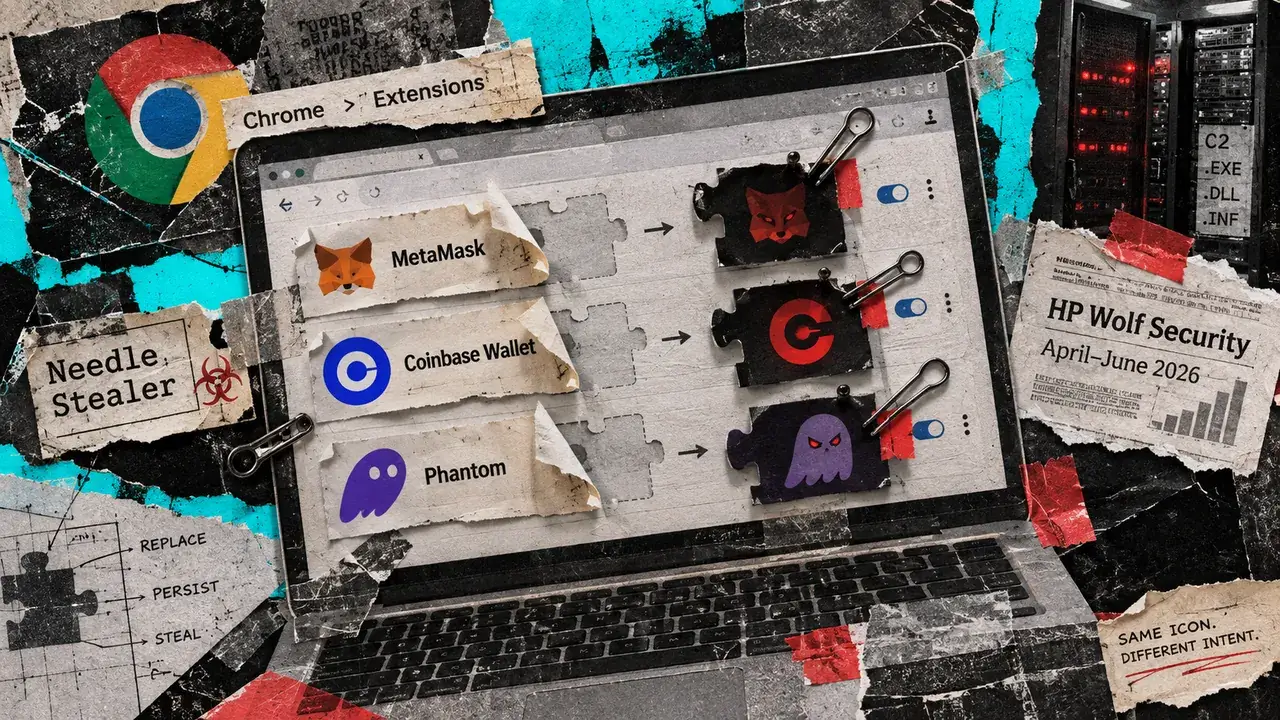
Fake AI Trading Bot Installs Needle Stealer Malware to Hijack Browser Crypto Wallets

Zubiqo Take
QuoteThreads

"Wrapping malware in digitally signed Microsoft binaries proves that reputation-based security filters are little more than speed bumps for dedicated attackers."

Fake AI Trading Bot Installs Needle Stealer Malware to Hijack Browser Crypto Wallets
📷 Image Source: CryptoSlate

Executive Summary

  • •A fake AI trading bot distributed Needle Stealer malware to replace legitimate browser crypto wallets with credential-stealing copies.
  • •The malware targeted 7 specific wallets by bypassing Microsoft SmartScreen using a digitally signed OLEView executable.
  • •Attackers built realistic login screens to capture passwords and wallet IDs directly from compromised Windows machines.

Community Sentiment

1-Tap Vote

Key Developments & Data

HP's threat-research team identified a campaign where attackers used search-engine poisoning to promote a fake AI assistant called tradingclaw[.]pro. The downloaded installer contained a legitimate, digitally signed Microsoft OLE/COM Object Viewer executable that loaded a malicious DLL, allowing the payload to bypass SmartScreen reputation checks. Once running, Needle Stealer used process hollowing to enumerate Chromium browser extensions, checking 32-character IDs against a hardcoded list to locate 7 specific wallets, including Phantom, MetaMask, and Coinbase Wallet. The malware then shut down the browser and extracted a malicious copy into the existing extension folder, presenting victims with realistic counterfeit login screens. Any crypto wallet ID and password entered into the substituted extension was sent directly to a command-and-control server operated by the attackers. HP did not disclose aggregate crypto-loss figures or a total victim count for the campaign, which operated from April through June 2026.
Zubiqo Intelligence Briefing

Get the unfiltered signal before markets open.

Top tech breakthroughs, venture funding, and market moves—synthesized into a 2-minute morning read. Zero PR fluff.

✓ 100% Free•✓ 1-click unsubscribe•✓ No spam ever

Zubiqo Strategic Assessment

Primary Impact

Retail crypto investors relying on browser-based hot wallets on Windows machines are most vulnerable to complete local credential compromise.

Strategic Shift

Attackers are successfully weaponizing the current hype around personalized AI trading strategies to trick users into manually bypassing standard operational security.

The Ripple Effect

Browser vendors will likely face mounting pressure to implement stricter runtime integrity checks for locally installed extensions to prevent on-disk swapping.

This intelligence assessment is generated by Zubiqo's AI for informational purposes only.
#malware#crypto#browser#phishing#security
Read original on CryptoSlate
Zubiqo MethodologyVerified Signal

Synthesized across 1,500+ daily market sources with human editorial oversight under Zubiqo's standards.

Event Magnitude6 / 10

Intelligence Quality Rating

Grade this brief: Is this actionable intelligence or market noise?

1-tap to rateAccidental scroll immune
Share

Read Next

ShinyHunters Breaches Rival Ransomware Gang Clop, Threatens 72-Hour Extortion Deadline
Cybersecurity

ShinyHunters Breaches Rival Ransomware Gang Clop, Threatens 72-Hour Extortion Deadline

LTFRB Takes Records System Offline Following 7.7GB Data Breach Claims
Cybersecurity

LTFRB Takes Records System Offline Following 7.7GB Data Breach Claims

Stay on the wire

Breaking tech, AI, and market intelligence the moment it happens. Zero fluff.

Live Broadcasts
TelegramXThreadsBlueskyMastodon
Critical 9.8 CVSS Orkes Conductor Flaw Under Active Exploitation
Cybersecurity

Critical 9.8 CVSS Orkes Conductor Flaw Under Active Exploitation

CISA Flags 3 Actively Exploited Linux Kernel Flaws, Imposes Weekend Patch Deadline
Cybersecurity

CISA Flags 3 Actively Exploited Linux Kernel Flaws, Imposes Weekend Patch Deadline

Zubiqo Methodology

Verified Signal

Synthesized across 1,500+ daily market sources with human editorial oversight under Zubiqo's standards.

Event Magnitude6 / 10

Related Briefs

Cybersecurity

ShinyHunters Breaches Rival Ransomware Gang Clop, Threatens 72-Hour Extortion Deadline

Sep 19
Cybersecurity

LTFRB Takes Records System Offline Following 7.7GB Data Breach Claims

Sep 19
Cybersecurity

Critical 9.8 CVSS Orkes Conductor Flaw Under Active Exploitation

Sep 19
Cybersecurity

CISA Flags 3 Actively Exploited Linux Kernel Flaws, Imposes Weekend Patch Deadline

Sep 19