Executive Summary
- •OneKey security researchers reproduced a transaction replacement attack against Ledger's outdated Ethereum app in a lab environment.
- •Ledger patched the vulnerability in version 1.22.2 on August 13 and confirmed zero user funds were lost.
- •The exploit required host-level compromise and targeted the signing process rather than seed generation.
Community Sentiment
AFFILIATE PARTNEROpen-Source Firmware • Cold Storage
Self-custody your Bitcoin & crypto with Trezor
Get Trezor
Affiliate disclosure: We may earn a commission if you purchase through this link.
Key Developments & Data
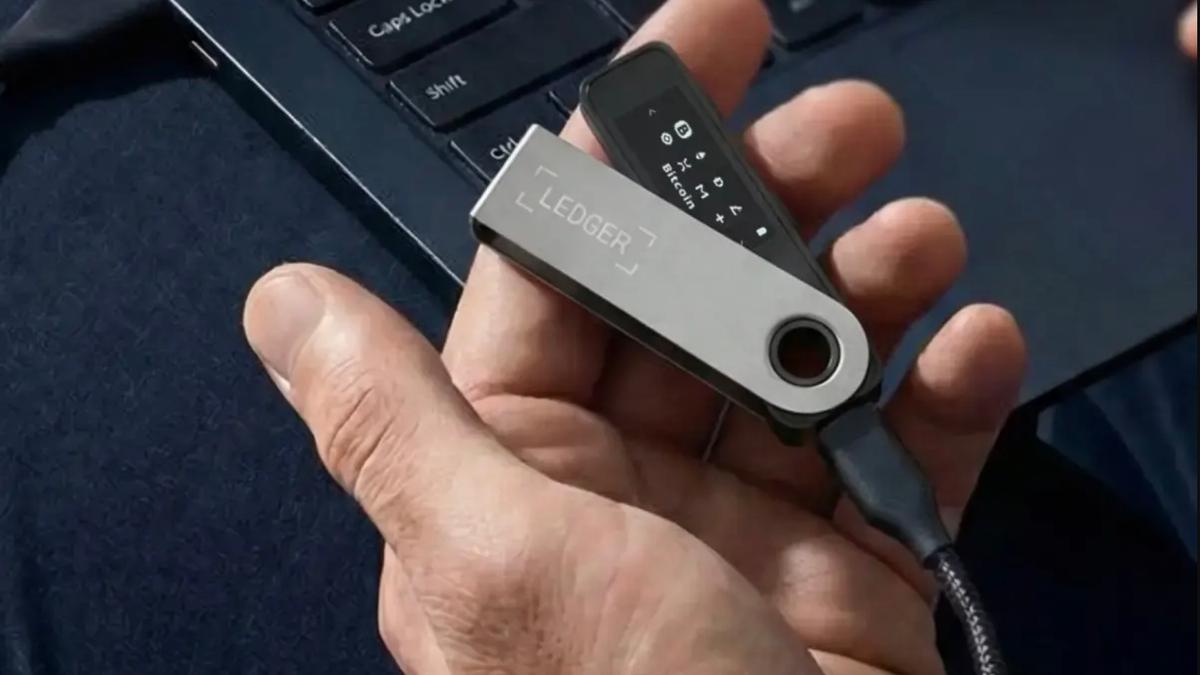
OneKey founder Yishi Wang announced the company's in-house security team executed a transaction replacement attack against Ledger's Ethereum app version 1.22.1.
The exploit targeted how transactions are handled during the signing process, allowing an attacker to overwrite the pending transaction while the user reviews the legitimate one.
Ledger clarified the vulnerability required control over device-host communications via malware, hostile webpages, or compromised wallet software.
The manufacturer patched the vulnerability with app-level safeguards in version 1.22.2 on August 13, and fixed the underlying issue in Secure SDK 26.6.1 on August 21.
"No Ledger user was hacked. What’s described here is a lab reproduction of a vulnerability in an outdated version of the Ethereum app." — Ledger
Zubiqo Strategic Assessment
Primary Impact
Retail crypto investors and hardware wallet manufacturers relying on secure transaction signing architectures.
Strategic Shift
Security disclosures are increasingly being weaponized as competitive marketing tools between rival hardware wallet manufacturers.
The Ripple Effect
Ledger will likely accelerate forced firmware and app updates through Ledger Live to prevent competitors from demonstrating exploits on legacy software.
This intelligence assessment is generated by Zubiqo's AI for informational purposes only.
Intelligence Quality Rating
Grade this brief: Slide & release to submit rating, or tap a preset.
🔥High Impact75/100
Slide & release to voteImmune to accidental scroll
Zubiqo Briefing
The daily signal, delivered every weekday.
A concise weekday briefing on AI, technology and business. Zero PR fluff.
Subscribe directly on Substack
Subscription completes on Substack • Free • 1-click unsubscribe anytime
✓ Free on Substack✓ Official Substack enrollment✓ 1-click unsubscribe