ZUBIQO.
AI & MLCryptoFinanceBig TechAI Models
CybersecurityGamingEVs & Clean EnergyRoboticsAerospaceBiotech & Health
Enterprise
ZUBIQO.

High-magnitude intelligence briefs for the tech and finance sectors. Zero fluff. Maximum signal.

[email protected]
X (Twitter)ThreadsTelegramBlueskyMastodon

Sections

  • AI & ML
  • Crypto
  • Finance
  • Big Tech
  • Cybersecurity
  • Gaming
  • EVs & Clean Energy
  • Robotics
  • Aerospace
  • Biotech & Health

Publication

  • About Us
  • Editorial Ethics
  • Partner With Us
  • Contact Us

Tools

  • AI Models Pricing

Legal

  • Privacy Policy
  • Terms of Service
  • Fair Use & DMCA

Disclaimer:Zubiqo Intelligence operates as a technology-enabled news and research publication under human editorial oversight. The news briefs, market analysis, "Magnitude Scores", and "Community Sentiment" metrics provided on this platform are strictly for informational and educational purposes only. They do not constitute financial, legal, investment, or trading advice. Cryptocurrencies and financial markets are highly volatile; always conduct your own research and consult with a licensed professional before making any investment decisions. By using this site, you agree to our Terms of Service.

© 2026 Zubiqo Intelligence. All rights reserved.

CybersecurityMAG 7Bearish
•
2026-08-10•1 min read

North Korean Hackers Build Offline AI Stack to Automate Malware

Zubiqo Take
QuoteThreads

"Nation-state adversaries no longer need to train custom frontier models when they can simply weaponize off-the-shelf open-source architecture to modernize their operations."

North Korean Hackers Build Offline AI Stack to Automate Malware
📷 Image Source: The Hacker News

Executive Summary

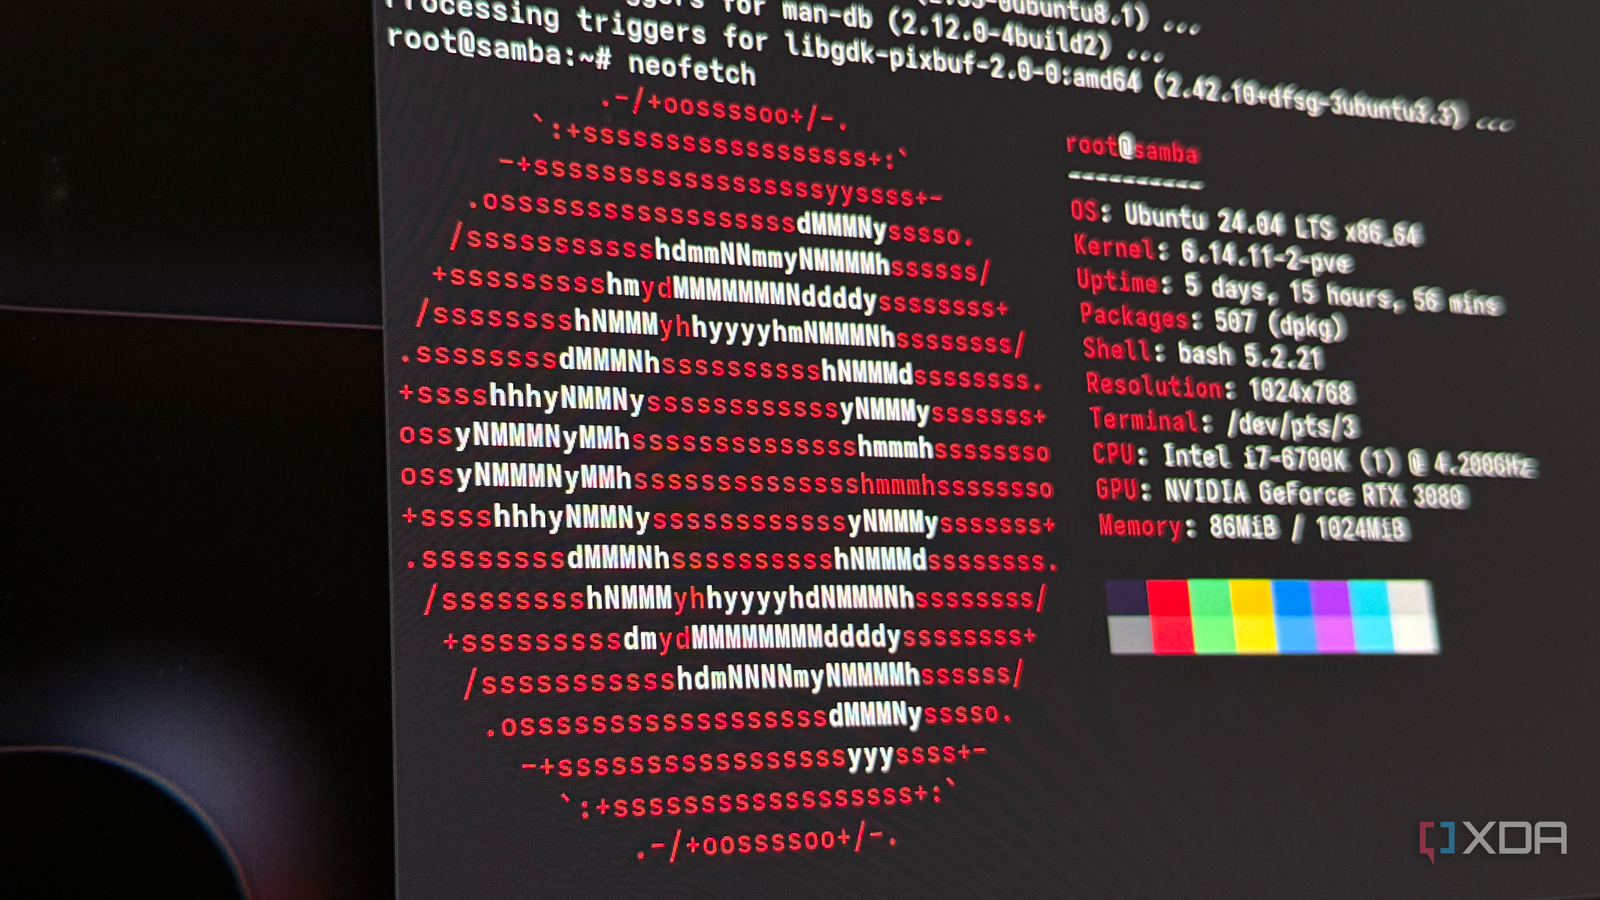
  • •South Korean security firm Genians discovered the espionage group actively running local tools like Ollama, GPT4All, and Msty to evade public chatbot monitoring.
  • •The infrastructure includes Microsoft Semantic Kernel, OpenAI's Whisper, and Cursor to integrate AI functions directly into custom C# and .NET payloads.
  • •Researchers recovered a configured Retrieval-Augmented Generation (RAG) database, allowing the unit to query private documents entirely offline.

Community Sentiment

1-Tap Vote

Key Developments & Data

North Korean hacking unit Kimsuky deploys offline AI models on proprietary servers to automate malware development. South Korean security firm Genians discovered the espionage group actively running local tools like Ollama, GPT4All, and Msty to evade public chatbot monitoring. The infrastructure includes Microsoft $MSFT Semantic Kernel, OpenAI's Whisper, and Cursor to integrate AI functions directly into custom C# and .NET payloads. Researchers recovered a configured Retrieval-Augmented Generation (RAG) database, allowing the unit to query private documents entirely offline. Traditional phishing tells like clumsy formatting and stilted translations will disappear from this attack chain.
Zubiqo Intelligence Briefing

Get the unfiltered signal before markets open.

Top tech breakthroughs, venture funding, and market moves—synthesized into a 2-minute morning read. Zero PR fluff.

✓ 100% Free•✓ 1-click unsubscribe•✓ No spam ever

Zubiqo Strategic Assessment

Primary Impact

Enterprise security operations centers (SOCs) and defense contractors, who can no longer rely on linguistic errors to filter out nation-state spear-phishing campaigns.

Strategic Shift

The offensive cyber landscape is shifting from cloud-dependent LLM exploitation to fully offline, self-hosted AI stacks that leave zero external telemetry.

The Ripple Effect

Endpoint detection platforms will be forced to aggressively pivot toward behavioral monitoring for LNK execution and PowerShell anomalies as initial email lures become indistinguishable from legitimate communications.

This intelligence assessment is generated by Zubiqo's AI for informational purposes only.

Intelligence Quality Rating

Grade this brief: Slide & release to submit rating, or tap a preset.
🔥High Impact75%
Slide & release to voteImmune to accidental scroll
#kimsuky#ai#malware#phishing#cybersecurity
Read original on The Hacker News
Zubiqo MethodologyVerified Signal

Synthesized across 1,500+ daily market sources with human editorial oversight under Zubiqo's standards.

Event Magnitude7 / 10
Share

Read Next

77% of Ransomware Groups Now Target Healthcare Amid 2026 Cyber Surge
Cybersecurity

77% of Ransomware Groups Now Target Healthcare Amid 2026 Cyber Surge

Canonical Forces 2-Week Ubuntu Patch Cycle to Survive AI Bug Flood
Cybersecurity

Canonical Forces 2-Week Ubuntu Patch Cycle to Survive AI Bug Flood

Stay on the wire

Breaking tech, AI, and market intelligence the moment it happens. Zero fluff.

Live Broadcasts
TelegramXThreadsBlueskyMastodon
OpenAI Grants Ukraine Access to Daybreak Cyber-Defense AI Tool
Cybersecurity

OpenAI Grants Ukraine Access to Daybreak Cyber-Defense AI Tool

FBI Probes Alleged ShinyHunters Hack Compromising Employee Data
Cybersecurity

FBI Probes Alleged ShinyHunters Hack Compromising Employee Data

Zubiqo Methodology

Verified Signal

Synthesized across 1,500+ daily market sources with human editorial oversight under Zubiqo's standards.

Event Magnitude7 / 10

Related Briefs

Cybersecurity

77% of Ransomware Groups Now Target Healthcare Amid 2026 Cyber Surge

Sep 24
Cybersecurity

Canonical Forces 2-Week Ubuntu Patch Cycle to Survive AI Bug Flood

Sep 24
Cybersecurity

OpenAI Grants Ukraine Access to Daybreak Cyber-Defense AI Tool

Sep 24
Cybersecurity

FBI Probes Alleged ShinyHunters Hack Compromising Employee Data

Sep 24