Executive Summary
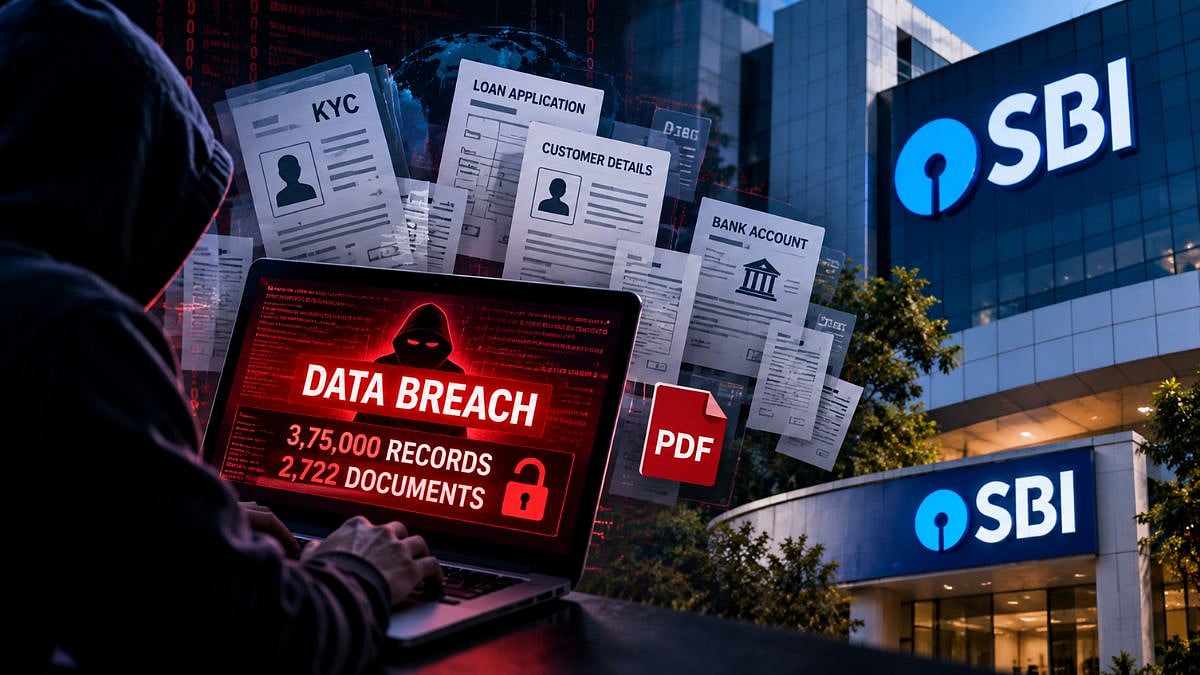
- •A threat actor named "Siriusim" claimed on BreachForums to have hacked customer records and PDF documents allegedly linked to the State Bank of India (SBI) and potentially its subsidiaries.
- •The listing claims 375,000 CSV rows (3.75 lakh customer records) and 2,722 PDF documents, with four verified samples containing valid phone numbers, CKYC details, and a matching KYC photograph.
- •The source and full authenticity of the dataset remain unconfirmed, including whether the files originated directly from SBI, a subsidiary, or a third-party service provider.
Community Sentiment
Encrypt your connection and network traffic with NordVPN
Key Developments & Data
Zubiqo Strategic Assessment
Primary Impact
Indian retail banking applicants and financial institutions, specifically individuals whose loan and KYC documentation may be exposed to identity theft, targeted phishing, and impersonation.
Strategic Shift
Centralized digital onboarding workflows—incorporating CKYC, video verification, and third-party application processing—concentrate high-value identity and income documents that cannot be easily rotated like passwords once exposed.
The Ripple Effect
If the dataset is authentic, affected applicants face heightened risks of fraudulent loan applications and impersonation using matched photographs, income declarations, and verified phone numbers.
This intelligence assessment is generated by Zubiqo's AI for informational purposes only.
Intelligence Quality Rating
Grade this brief: Slide & release to submit rating, or tap a preset.
The daily signal, delivered every weekday.
A concise weekday briefing on AI, technology and business. Zero PR fluff.
Subscription completes on Substack • Free • 1-click unsubscribe anytime