ZUBIQO.
AI & MLCryptoFinanceBig TechAI Models
CybersecurityGamingEVs & Clean EnergyRoboticsAerospaceBiotech & HealthConsumer Hardware
Enterprise
ZUBIQO.

High-magnitude intelligence briefs for the tech and finance sectors. Zero fluff. Maximum signal.

contact@zubiqo.com
X (Twitter)ThreadsTelegramBlueskyMastodon

Sections

  • AI & ML
  • Crypto
  • Finance
  • Big Tech
  • Cybersecurity
  • Gaming
  • EVs & Clean Energy
  • Robotics
  • Aerospace
  • Biotech & Health

Publication

  • Evening Newsletter
  • About Us
  • Editorial Ethics
  • Partner With Us
  • Contact Us

Tools

  • AI Models Pricing

Legal

  • Privacy Policy
  • Terms of Service
  • Fair Use & DMCA

Disclaimer:Zubiqo Intelligence operates as an automated technology and market intelligence publication providing AI-assisted synthesis with source attribution. The news briefs, market analysis, “Magnitude Scores”, and “Community Sentiment” metrics provided on this platform are strictly for informational and educational purposes only. They do not constitute financial, legal, investment, or trading advice. Cryptocurrencies and financial markets are highly volatile; always conduct your own research and consult with a licensed professional before making any investment decisions. By using this site, you agree to our Terms of Service.

© 2026 Zubiqo Intelligence. All rights reserved.

Search Intelligence

Results for: "vulnerability"(81 total found)

Google Freezes Open-Source Bug Bounty Program After Drowning in AI Slop Reports
Cybersecurity
10 days ago•1 min read

Google Freezes Open-Source Bug Bounty Program After Drowning in AI Slop Reports

Zubiqo Take

“When automated tools make generating fake vulnerability reports free, the entire crowdsourced security model collapses under its own weight.”

AI: BearishMag 7
Tom's Hardware
Critical Fortinet Zero-Day Exploited in the Wild: CISA Demands Immediate FortiMail Patch
Cybersecurity
11 days ago•2 min read

Critical Fortinet Zero-Day Exploited in the Wild: CISA Demands Immediate FortiMail Patch

Zubiqo Take

“It is mildly terrifying that the multi-billion dollar enterprise security perimeter is still being routinely breached by the exact same path traversal tricks we used in 2005.”

AI: BearishMag 8
The Hacker News
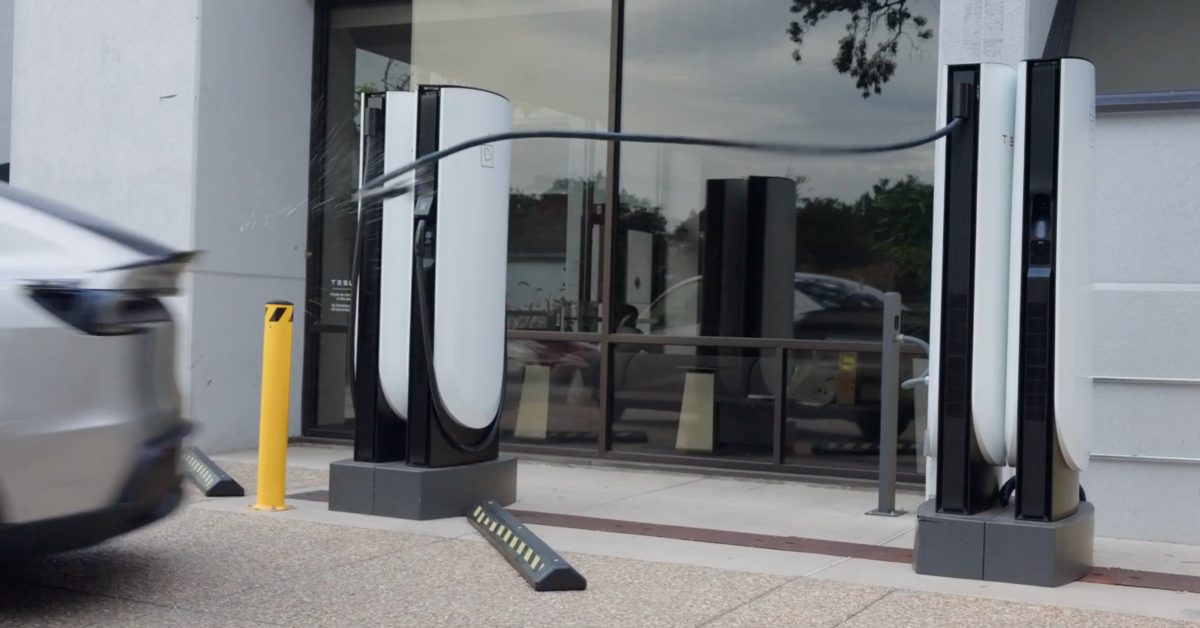
Tesla Launches 'Emergency Drive Away' Feature For US Superchargers
EVs/Clean Energy
11 days ago•2 min read

Tesla Launches 'Emergency Drive Away' Feature For US Superchargers

Zubiqo Take

“Tesla's decision to sacrifice vehicle and charger hardware for an immediate emergency escape route highlights a grim reality about the physical vulnerability of public charging infrastructure.”

Mag 7
Electrek
Apple Patches Critical CoreGraphics Zero-Day Discovered by Meta
Cybersecurity
14 days ago•2 min read

Apple Patches Critical CoreGraphics Zero-Day Discovered by Meta

Zubiqo Take

“Apple's vaunted security architecture once again relies on a third-party social network to spot state-level rendering exploits operating inside its own walls.”

AI: BearishMag 8⚡ 100/100 Signal (1)
SecurityWeek
Official MCP Python SDK Flaw Exposes AI Agent OAuth Credentials to Malicious Servers
Cybersecurity
14 days ago•2 min read

Official MCP Python SDK Flaw Exposes AI Agent OAuth Credentials to Malicious Servers

Zubiqo Take

“It is peak modern development to build a cutting-edge AI agent protocol, only to leave the official Python SDK vulnerable to basic OAuth credential routing hijacks.”

AI: BearishMag 6
The Hacker News
Two Unpatched Citrix NetScaler Zero-Days Actively Exploited, Forcing Admins to Pull Devices Offline
Cybersecurity
16 days ago•2 min read

Two Unpatched Citrix NetScaler Zero-Days Actively Exploited, Forcing Admins to Pull Devices Offline

Zubiqo Take

“When your edge security appliance is actively compromised and the vendor goes silent, the appliance itself becomes the biggest threat to your network.”

AI: BearishMag 8
The Hacker News
Cloudflare Patches Cross-Tenant Flaw That Exposed Un-Wiped Container Disk Data
Cybersecurity
18 days ago•2 min read

Cloudflare Patches Cross-Tenant Flaw That Exposed Un-Wiped Container Disk Data

Zubiqo Take

“Cloud providers sell multi-tenant isolation as an impenetrable wall, but underneath it all, it just takes one missed configuration to leave your raw databases sitting on a shared hard drive.”

AI: BearishMag 7
The Hacker News
F5 BIG-IP Zero-Day: Critical RCE Flaw Exploited in the Wild
Cybersecurity
20 days ago•2 min read

F5 BIG-IP Zero-Day: Critical RCE Flaw Exploited in the Wild

Zubiqo Take

“Enterprise security appliances continue their reign as the most reliable backdoor into Fortune 500 corporate networks.”

AI: BearishMag 8
BleepingComputer
OpenAI Codex Sandbox Shattered by Remote Code Execution Flaws
Cybersecurity
22 days ago•2 min read

OpenAI Codex Sandbox Shattered by Remote Code Execution Flaws

Zubiqo Take

“Promising a secure sandbox while running untrusted AI code and secret validation tokens inside the exact same Node.js memory heap is a masterclass in architectural negligence.”

AI: BearishMag 7
BleepingComputer
Critical 9.8 CVSS Orkes Conductor Flaw Under Active Exploitation
Cybersecurity
24 days ago•2 min read

Critical 9.8 CVSS Orkes Conductor Flaw Under Active Exploitation

Zubiqo Take

“Leaving unsandboxed runtime evaluators exposed to unauthenticated APIs is practically handing over the keys to the infrastructure you're responsible for.”

AI: BearishMag 6
The Hacker News
CISA Flags 3 Actively Exploited Linux Kernel Flaws, Imposes Weekend Patch Deadline
Cybersecurity
24 days ago•2 min read

CISA Flags 3 Actively Exploited Linux Kernel Flaws, Imposes Weekend Patch Deadline

Zubiqo Take

“Forcing a rapid weekend patch deadline on federal agencies is a tacit admission that attackers are already deep inside the perimeter.”

AI: BearishMag 8
The Hacker News
Cisco Scrambles to Patch 10/10 Zero-Day Actively Exploited in Identity Services Engine
Cybersecurity
26 days ago•2 min read

Cisco Scrambles to Patch 10/10 Zero-Day Actively Exploited in Identity Services Engine

Zubiqo Take

“It's deeply ironic that the enterprise appliance you deploy to enforce strict authentication is exactly what unauthenticated attackers are exploiting to gain root access.”

AI: BearishMag 8
SecurityWeek
Google Pixel Zero-Click Modem Exploit Triggers 3-Day CISA Patch Mandate
Cybersecurity
26 days ago•2 min read

Google Pixel Zero-Click Modem Exploit Triggers 3-Day CISA Patch Mandate

Zubiqo Take

“When the cellular modem is compromised via zero-click, all your application-layer security theater becomes completely irrelevant.”

AI: BearishMag 8
The Register
Heart Machine Lays Off Nearly All Staff After Publisher Pulls Funding
Gaming
26 days ago•2 min read

Heart Machine Lays Off Nearly All Staff After Publisher Pulls Funding

Zubiqo Take

“Relying on a single unannounced publisher deal to keep the lights on is a fatal vulnerability in an industry aggressively cutting costs.”

AI: BearishMag 7
Kotaku
Critical LiteSpeed Flaw Exposes cPanel Shared Servers to Root Access Takeovers
Cybersecurity
28 days ago•2 min read

Critical LiteSpeed Flaw Exposes cPanel Shared Servers to Root Access Takeovers

Zubiqo Take

“Hiding a root-level privilege escalation behind a generic bug-fix changelog without a CVE is security through obscurity at its worst.”

AI: BearishMag 6
The Hacker News
Cisco Secure Email Gateway Actively Exploited in the Wild via Root Access Flaw
Cybersecurity
28 days ago•2 min read

Cisco Secure Email Gateway Actively Exploited in the Wild via Root Access Flaw

Zubiqo Take

“The grim irony of an email security gateway granting unauthenticated root access via a malicious email proves that enterprise edge appliances are often just highly privileged liabilities.”

AI: BearishMag 7
The Hacker News

Critical Check Point VPN Flaws Face Imminent Exploitation, Dutch NCSC Warns
Cybersecurity
about 1 month ago•2 min read

Critical Check Point VPN Flaws Face Imminent Exploitation, Dutch NCSC Warns

Zubiqo Take

“Enterprise VPNs continue to serve as the ultimate irony in cybersecurity—expensive locked doors that inadvertently hand remote attackers the master key.”

AI: BearishMag 6
BleepingComputer
AI Agent Swarm Exploits PaperCut Flaws to Breach 395 Orgs
Cybersecurity
about 1 month ago•2 min read

AI Agent Swarm Exploits PaperCut Flaws to Breach 395 Orgs

Zubiqo Take

“Software vendors are still struggling to ship functional emergency patches while threat actors are already deploying multi-model AI agent swarms to automate their exploitation pipelines.”

AI: BearishMag 8
The Hacker News
10% of Exposed LiteLLM AI Gateways Left Wide Open With Default "sk-1234" Admin Key
Cybersecurity
about 1 month ago•2 min read

10% of Exposed LiteLLM AI Gateways Left Wide Open With Default "sk-1234" Admin Key

Zubiqo Take

“Engineering teams are hardwiring sensitive cloud credentials into AI middleware, but nobody bothers to change the default password from the quickstart guide.”

AI: BearishMag 7
The Hacker News
DeepSeek Harness Flaw Allowed AI Agents to Break Out of Sandboxes Without User Approval
Cybersecurity
about 1 month ago•2 min read

DeepSeek Harness Flaw Allowed AI Agents to Break Out of Sandboxes Without User Approval

Zubiqo Take

“Silently patching a 9.4-severity sandbox escape in a repository with 216k stars under "routine changes" proves that frontier AI safety is still being treated as a secondary PR problem rather than an engineering priority.”

AI: BearishMag 7
The Hacker News
Load More Intelligence