ZUBIQO.
AI & MLCryptoFinanceBig TechAI Models
CybersecurityGamingEVs & Clean EnergyRoboticsAerospaceBiotech & HealthConsumer Hardware
Enterprise
ZUBIQO.

High-magnitude intelligence briefs for the tech and finance sectors. Zero fluff. Maximum signal.

contact@zubiqo.com
X (Twitter)ThreadsTelegramBlueskyMastodon

Sections

  • AI & ML
  • Crypto
  • Finance
  • Big Tech
  • Cybersecurity
  • Gaming
  • EVs & Clean Energy
  • Robotics
  • Aerospace
  • Biotech & Health

Publication

  • Evening Newsletter
  • About Us
  • Editorial Ethics
  • Partner With Us
  • Contact Us

Tools

  • AI Models Pricing

Legal

  • Privacy Policy
  • Terms of Service
  • Fair Use & DMCA

Disclaimer:Zubiqo Intelligence operates as an automated technology and market intelligence publication providing AI-assisted synthesis with source attribution. The news briefs, market analysis, “Magnitude Scores”, and “Community Sentiment” metrics provided on this platform are strictly for informational and educational purposes only. They do not constitute financial, legal, investment, or trading advice. Cryptocurrencies and financial markets are highly volatile; always conduct your own research and consult with a licensed professional before making any investment decisions. By using this site, you agree to our Terms of Service.

© 2026 Zubiqo Intelligence. All rights reserved.

  1. Home
  2. /
  3. Cybersecurity
  4. /
  5. Canva Confirms Third-Party Canny Breach Exposed Enterprise Salesforce Records
CybersecurityMAG 7AI: Bearish
•
2026-10-19•2 min read

Canva Confirms Third-Party Canny Breach Exposed Enterprise Salesforce Records

Zubiqo Take
QuoteThreads

“Locking down your core platform means very little when a peripheral product-feedback integration still has a direct pipe into your Salesforce records.”

Canva Confirms Third-Party Canny Breach Exposed Enterprise Salesforce Records
📷 Image Source: Cyber Daily

Executive Summary

  • •Canva confirmed that unauthorized access to third-party feedback tool Canny exposed some enterprise customer records via its connection to Canva's Salesforce account.
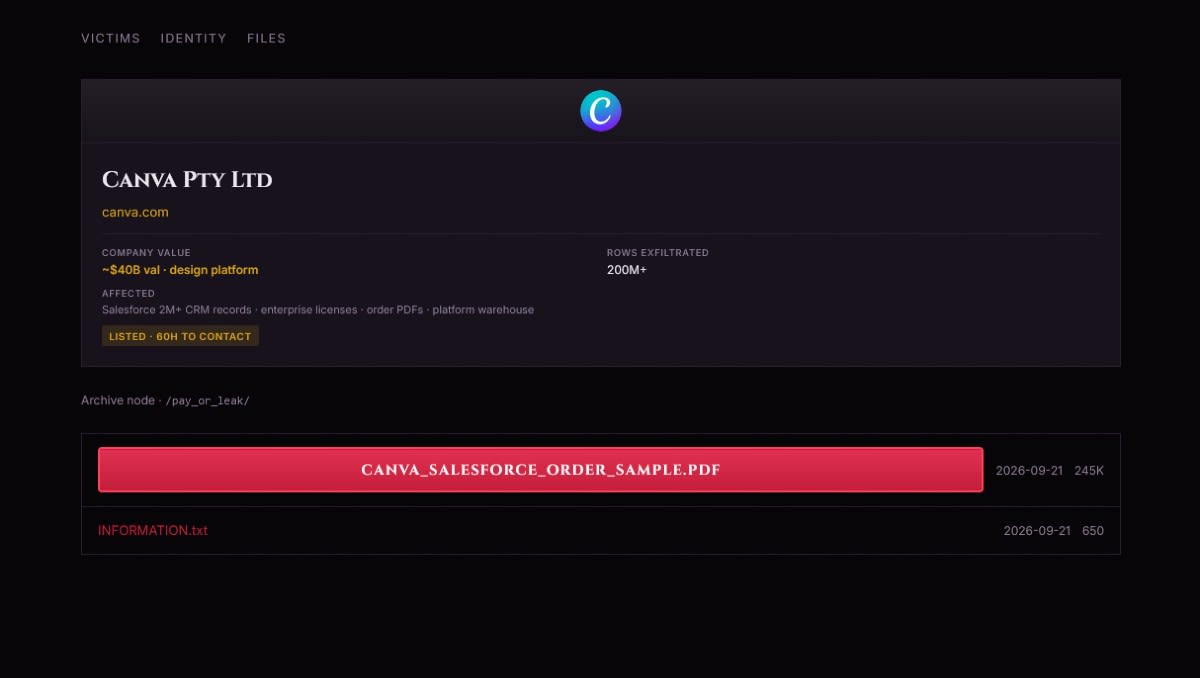
  • •The Seven Deadly Sins ransomware group claims the allegedly compromised data includes more than 2M Salesforce records, enterprise license orders, and billing PDFs.
  • •Canva revoked Canny's access and stated that its core platform, user passwords, designs, and content were not compromised.

Community Sentiment

1-Tap Vote
NordVPN
AFFILIATE PARTNER30-Day Money-Back Policy • Encrypted Traffic

Encrypt your connection and network traffic with NordVPN

Get NordVPN
Affiliate disclosure: We may earn a commission if you subscribe through this link.

Key Developments & Data

Australian software company Canva has disclosed that some enterprise customer records were exposed after unauthorized access hit Canny, a third-party product feedback tool connected to Canva's Salesforce account. The Seven Deadly Sins ransomware group claimed the breach in an October 16 post on its darknet leak site, alleging the compromised data includes more than 2M Salesforce records, enterprise license orders, and billing PDFs. The group published one sample document appearing to be a Canva for Enterprise order form and claimed the stolen data has already been sold to an unidentified private buyer. Canva stated that the exposed records included business contact details and routine business documentation, adding that it immediately revoked Canny's access, notified affected customers where required, and confirmed its core platform, passwords, and user designs remain secure. "The unauthorised access to Canny allowed access to some enterprise customer records through its connection to Canva’s Salesforce account, including business contact details and routine business documentation." — Canva Spokesman

Zubiqo Strategic Assessment

Primary Impact

Canva enterprise customers whose business contact details and routine documentation were exposed via the Canny integration, along with SaaS vendors relying on third-party CRM connectors.

Strategic Shift

Enterprise security risk continues to concentrate around peripheral SaaS integrations and feedback tools that hold broad read permissions into core CRM databases like Salesforce.

The Ripple Effect

Enterprise security teams may tighten API token scopes and audit third-party tools connected to Salesforce environments, while affected Canva enterprise clients face heightened phishing or social engineering risks from exposed billing and contact records.

This intelligence assessment is generated by Zubiqo's AI for informational purposes only.

Intelligence Quality Rating

Grade this brief: Slide & release to submit rating, or tap a preset.

🔥High Impact75/100
Slide & release to voteImmune to accidental scroll
Zubiqo Briefing

The daily signal, delivered every weekday.

A concise weekday briefing on AI, technology and business. Zero PR fluff.

Subscribe directly on Substack↗

Subscription completes on Substack • Free • 1-click unsubscribe anytime

✓ Free on Substack•✓ Official Substack enrollment•✓ 1-click unsubscribe
#canva#salesforce#cybersecurity#data breach
Read original on Cyber Daily
Zubiqo MethodologyAI Synthesis

Synthesized from linked market reporting using AI extraction under Zubiqo's editorial standards. Have a correction? Contact our desk.

Event Magnitude7 / 10
Share

Read Next

South Korean Coffee Chain Hollys Discloses Data Breach Exposing 2.76M Customer Info Pieces
Cybersecurity

South Korean Coffee Chain Hollys Discloses Data Breach Exposing 2.76M Customer Info Pieces

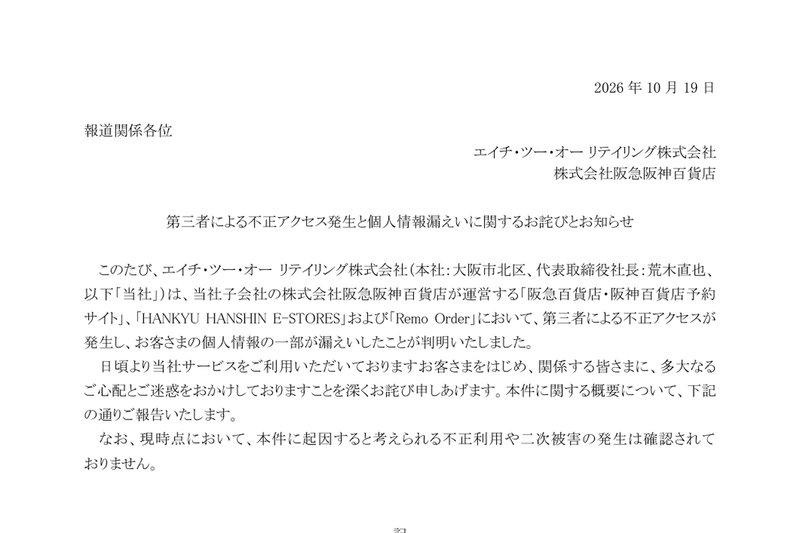
Hankyu Hanshin Department Store and H2O Retailing Breach Hits ~1.26M Member Records
Cybersecurity

Hankyu Hanshin Department Store and H2O Retailing Breach Hits ~1.26M Member Records

Stay on the wire

Breaking tech, AI, and market intelligence the moment it happens. Zero fluff.

Live Broadcasts
TelegramXThreadsBlueskyMastodon
Qubic Halts Mainnet After Weak Wallet Seeds Drain $1.3M From 1,404 Accounts
Crypto

Qubic Halts Mainnet After Weak Wallet Seeds Drain $1.3M From 1,404 Accounts

Cysic Halts Cross-Chain Bridge After Unauthorized Mint of 10M CYS on BNB Chain
Cybersecurity

Cysic Halts Cross-Chain Bridge After Unauthorized Mint of 10M CYS on BNB Chain

Zubiqo Methodology

AI Synthesis

Synthesized from linked market reporting using AI extraction under Zubiqo's editorial standards. Have a correction? Contact our desk.

Event Magnitude7 / 10

Related Briefs

Cybersecurity

South Korean Coffee Chain Hollys Discloses Data Breach Exposing 2.76M Customer Info Pieces

Oct 19
Cybersecurity

Hankyu Hanshin Department Store and H2O Retailing Breach Hits ~1.26M Member Records

Oct 19
Crypto

Qubic Halts Mainnet After Weak Wallet Seeds Drain $1.3M From 1,404 Accounts

Oct 18
Cybersecurity

Cysic Halts Cross-Chain Bridge After Unauthorized Mint of 10M CYS on BNB Chain

Oct 18
Crypto

Ledger CEO Pascal Gauthier and Mark Karpelès Clash Over $90M Hardware Implant Losses

Oct 18
Cybersecurity

More Rewards Loyalty Program Confirms Data Breach Affecting Save-On-Foods Shoppers

Oct 18