Executive Summary
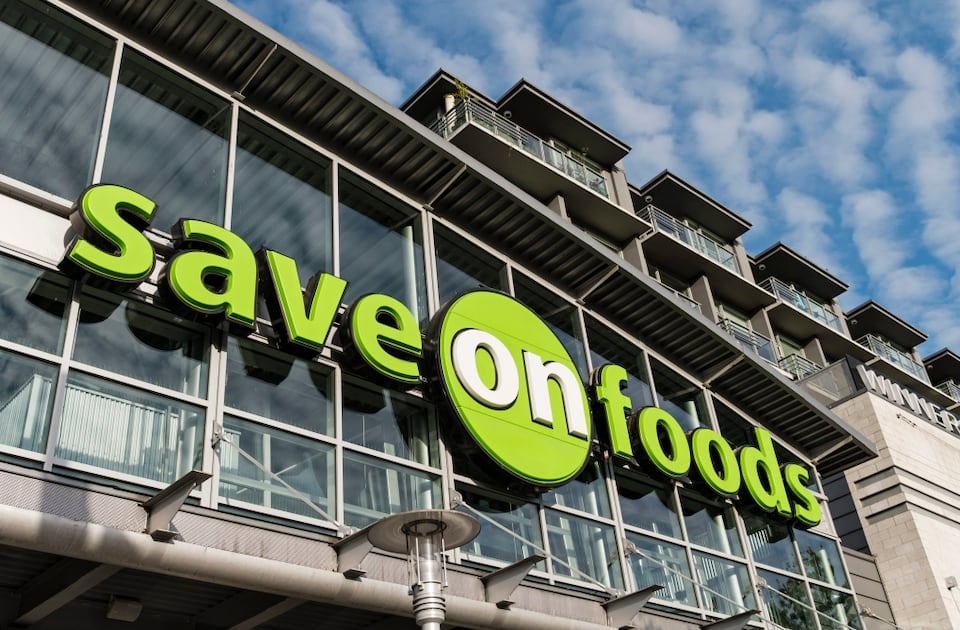
- •More Rewards confirmed a cybersecurity breach exposed customer personal information from its loyalty database used by Save-On-Foods and other Jim Pattison-owned grocers.
- •Accessed data includes names and, if provided, addresses, phone numbers, email addresses, and dates of birth, while the company declined to disclose the number of affected customers.
- •Passwords, credit card details, and transaction histories were not accessed, and the company has notified privacy regulators while warning customers about potential phishing scams.
Community Sentiment
Encrypt your connection and network traffic with NordVPN
Key Developments & Data
Zubiqo Strategic Assessment
Primary Impact
Western Canadian grocery shoppers using the More Rewards loyalty program across Save-On-Foods, Buy-Low Foods, and Quality Foods.
Strategic Shift
Retail loyalty databases centralize verified contact details and dates of birth, making them persistent targets for identity profiling even when payment systems are segregated.
The Ripple Effect
Affected customers face heightened exposure to targeted phishing and impersonation scams utilizing their verified contact details and birthdates.
This intelligence assessment is generated by Zubiqo's AI for informational purposes only.
Intelligence Quality Rating
Grade this brief: Slide & release to submit rating, or tap a preset.
The daily signal, delivered every weekday.
A concise weekday briefing on AI, technology and business. Zero PR fluff.
Subscription completes on Substack • Free • 1-click unsubscribe anytime