Executive Summary
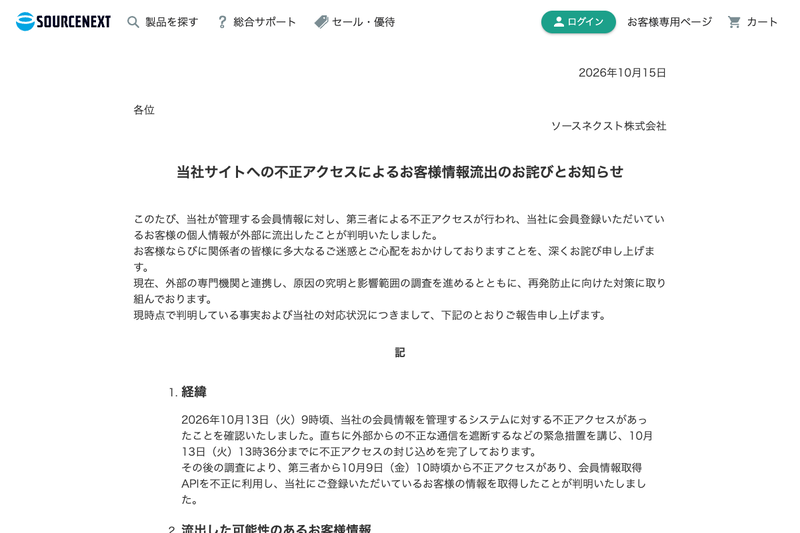
- •SOURCENEXT announced that unauthorized access to its member system potentially exposed widespread personal information.
- •The breach affects exactly 22,519,960 records, exposing passwords, addresses, and birth dates, though credit card data remains secure.
- •The company is urging immediate password resets to mitigate the risk of credential reuse on other platforms.
Community Sentiment
Encrypt your connection and network traffic with NordVPN
Key Developments & Data
Zubiqo Strategic Assessment
Primary Impact
SOURCENEXT users and enterprise clients whose contact details and company names were exposed, placing them at high risk for targeted social engineering.
Strategic Shift
The ongoing vulnerability of centralized identity and subscription management systems that pool comprehensive, plain-text PII.
The Ripple Effect
The simultaneous exposure of passwords and detailed PII will likely trigger a wave of credential stuffing attacks against secondary services where affected users reused their login credentials.
This intelligence assessment is generated by Zubiqo's AI for informational purposes only.
Intelligence Quality Rating
Grade this brief: Slide & release to submit rating, or tap a preset.
The daily signal, delivered every weekday.
A concise weekday briefing on AI, technology and business. Zero PR fluff.
Subscription completes on Substack • Free • 1-click unsubscribe anytime