
Search Intelligence
Results for: "patch"(95 total found)

Cybersecurity
•2 min read
AI Agent Swarm Exploits PaperCut Flaws to Breach 395 Orgs
Zubiqo Take
“Software vendors are still struggling to ship functional emergency patches while threat actors are already deploying multi-model AI agent swarms to automate their exploitation pipelines.”
AI: BearishMag 8
The Hacker News
Cybersecurity
•2 min read
Google Patches 7th Actively Exploited Chrome Zero-Day of 2026
Zubiqo Take
“Withholding bug details is standard protocol, but it also confirms the exploit is trivial enough that attackers don't need much of a head start once they see the patch diff.”
AI: BearishMag 8
BleepingComputer

Crypto
•2 min read
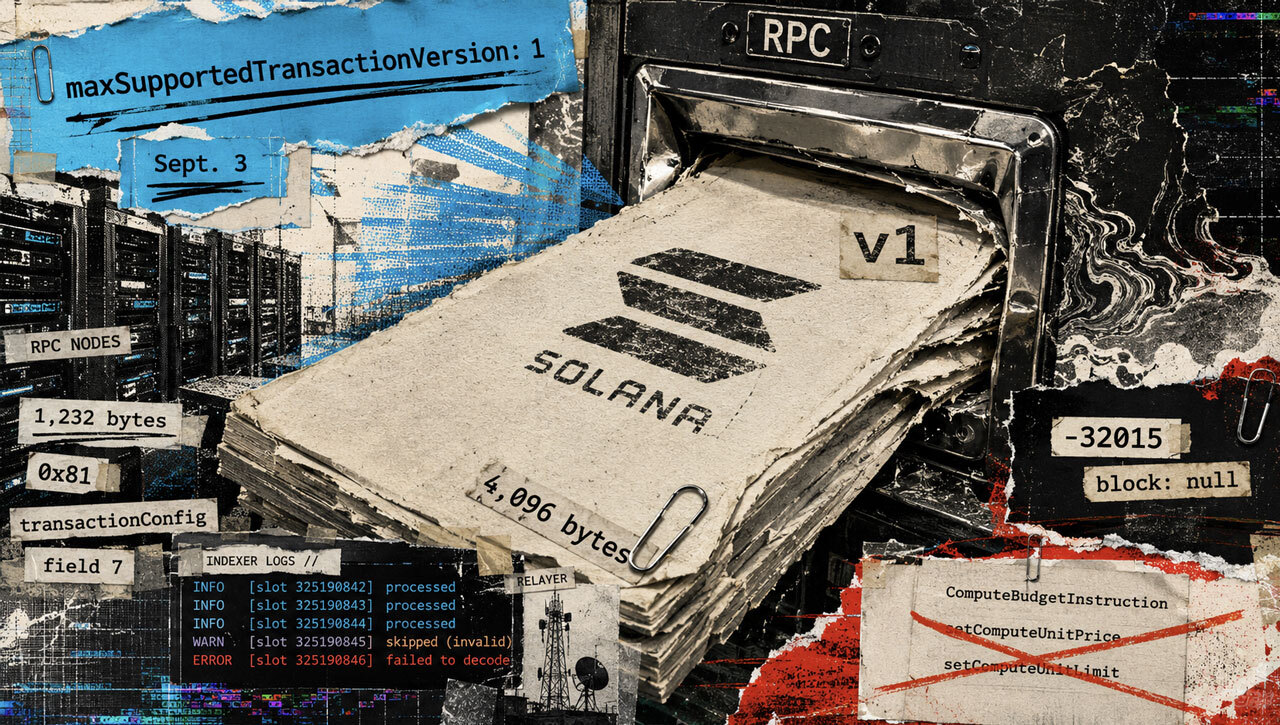
Solana V1 Upgrade Exposes Unpatched Infrastructure to Silent Fee Failures and RPC Freezes
Zubiqo Take
“It is always the silent application-layer structural changes that end up draining the wallets of infrastructure providers who ignore developer changelogs.”
AI: BearishMag 7
CryptoSlate
Cybersecurity
•2 min read
Google Patches Actively Exploited Chrome V8 Zero-Day (CVE-2026-85046)
Zubiqo Take
“Google tossing a $1,000 bounty to a researcher for catching an actively exploited V8 zero-day is a stark reminder that the white-hat market pays pennies compared to the dark web.”
AI: BearishMag 8
The Hacker News
Big Tech
•2 min read
Microsoft’s October Windows 11 Security Patch Will Tank Your Gaming Framerates
Zubiqo Take
“Shipping default security that kills performance and asking users to manually toggle it for games is just shifting the blame for the inevitable malware infections.”
AI: BearishMag 7
XDA Developers
Cybersecurity
•2 min read
Calix Router Flaw: Unpatched Vulnerability Exposes Home Networks to Hackers
Zubiqo Take
“Vendors ship hardware with wide-open WAN endpoints and leave ISPs to clean up the inevitable botnet mess.”
AI: BearishMag 7
BleepingComputer


Cybersecurity
•1 min read
Adobe Patches Three Critical CVSS 10.0 Flaws in ColdFusion and Commerce
Zubiqo Take
“Two maximum-severity execution flaws in the same legacy on-premise product within a fourteen-day window tells you exactly how fast technical debt is compounding.”
AI: BearishMag 7
The Hacker News
Cybersecurity
•2 min read
SAP Patches Critical CVSS 10.0 RCE Flaw in Commerce Cloud
Zubiqo Take
“A 10.0 unauthenticated RCE on an enterprise commerce platform is just handing the keys to anyone who's running a basic port scanner.”
AI: BearishMag 7
The Hacker News